
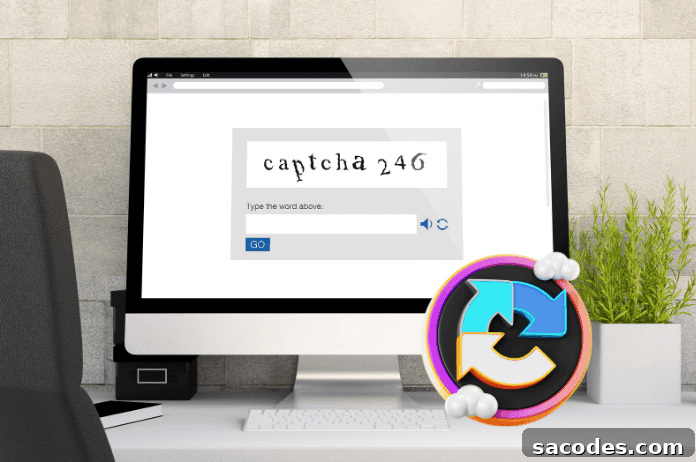
The conveniences of the digital age have brought new security challenges: as cyber threats and malicious software increase, websites and online platforms need stronger protection. Automated scripts, bots, and malware often try to create fake accounts, post spam, or misuse services. One widely used defense against these threats is CAPTCHA technology. Although many encounter CAPTCHAs regularly, their purpose and operation are not always clear. CAPTCHA (Completely Automated Public Turing test to tell Computers and Humans Apart) is an automated Turing test designed to distinguish humans from machines. In short, a CAPTCHA verifies that a user interacting with a site is a real person. This article explains what CAPTCHA is, how it works, its common uses, and practical considerations for implementation.
Importance and Common Uses of CAPTCHA
Many websites rely on CAPTCHA to guard against automated abuse. This protection is particularly important for areas that require user interaction, such as sign-up forms, online surveys, comments, and password recovery processes. Typical goals of CAPTCHA implementations include:
- Preventing Automated Registrations: Bots frequently create fake accounts to inflate metrics, spread spam, or exploit trial offers. CAPTCHA helps block those automated sign-ups.
- Protecting Digital Services: CAPTCHA reduces the risk of abuse against online services and applications, limiting spam submissions and automated attacks that degrade service quality.
- Stopping Automated Form Submissions: Forms used for contact, feedback, or transactions can be targeted by auto-fill scripts. CAPTCHA makes it harder for such automated tools to submit forms at scale.
Implementing effective CAPTCHA is part of a layered security approach: while it does not solve every threat, it raises the bar for attackers and reduces the volume of automated abuse site owners must handle.
How CAPTCHA Works
CAPTCHA systems typically require a user to complete a challenge that is easy for humans but difficult for automated programs. Challenges may be visual, auditory, or behavioral, and the core idea is to exploit differences between human and machine abilities.
As automated tools and machine learning have advanced, some simple CAPTCHAs have become easier for bots to bypass. In response, developers continue to refine CAPTCHA techniques to remain effective while minimizing friction for legitimate users.
Visual CAPTCHA: The most common form displays distorted characters—letters and numbers—or images that a user must identify and type. Deformations, noise, and overlapping elements make automated optical character recognition (OCR) more difficult, while humans can usually read the content.
Audio CAPTCHA: Provided as an alternative for users with visual impairments, audio CAPTCHAs present spoken characters or words. These are useful for accessibility but can be affected by background noise or speech recognition advances.
Image Recognition CAPTCHA: These challenges ask users to select images matching a prompt, such as “select all squares with traffic lights” or “click the pictures that contain a cat.” They rely on human visual understanding and context recognition.
Time-Based CAPTCHA: This technique measures how quickly a form is completed. Bots can fill fields in milliseconds; humans generally take longer. Timing heuristics help detect suspiciously fast submissions.
Motion and Interaction CAPTCHA: Users may be asked to drag an object, draw a shape, or complete a simple gesture. These interactions are more difficult for basic scripts to replicate.
Behavioral and Risk-Based Approaches: Some systems analyze user behavior—mouse movements, keystroke patterns, and browsing context—to assess whether a visitor is human. These approaches can be less intrusive, operating invisibly in the background while still blocking suspicious activity.
Challenges and Criticisms of CAPTCHA
Despite their benefits, CAPTCHAs have limitations and draw criticism. Accessibility is a major concern: purely visual CAPTCHAs can exclude users with visual impairments, while audio alternatives may fail in noisy environments or be hard to understand. Overly complex challenges can frustrate legitimate users and increase abandonment rates on forms and transactions.
Another challenge is the arms race between CAPTCHA developers and attackers. As machine learning improves, attackers can sometimes create tools that bypass simpler CAPTCHAs. Therefore, maintaining effectiveness requires continuous updates and a combination of techniques.
Site owners must balance security with user experience. Good practice includes providing accessible alternatives, minimizing unnecessary friction, and using CAPTCHAs as part of a multi-layered defense that includes rate limiting, IP reputation checks, and server-side validation.
Conclusion
In today’s digital environment, protecting websites and online services from automated abuse is essential. CAPTCHA remains a valuable tool in that effort, helping distinguish between human users and automated programs. However, effective implementation requires attention to accessibility, user experience, and evolving attack methods. By combining a variety of CAPTCHA techniques with other security measures, organizations can reduce automated threats while keeping interactions as seamless as possible for legitimate users.