
SSH Access and Usage on Linux Hosting
SSH (Secure Shell) is a protocol used to establish a secure connection to another computer over a network. On Linux hosting, SSH is commonly used for file transfers, database management, and a wide range of server administration tasks. This guide explains how to enable SSH access on Linux hosting, how to use it for everyday tasks, and best practices to keep your server secure.
Why SSH Access Matters
SSH provides an encrypted channel between your local machine and the server, protecting passwords and data from interception. For anyone managing websites, databases, or server configurations on Linux hosting, SSH is an essential tool because it allows precise, efficient, and secure control of the server environment.
How to Enable SSH Access
Many hosting providers disable SSH by default for security reasons. Below is a clear, step-by-step approach to enabling SSH on your Linux hosting account.
1. Contact Your Hosting Provider
The first step is to confirm whether SSH access is available and how it can be activated.
- Control Panel: Many providers offer an option to enable SSH through control panels such as cPanel or Plesk. Look under “Advanced” or “Security” sections for options like “SSH Access” or “Terminal.”
- Support Team: If you cannot find an SSH option in your control panel, contact customer support and request SSH access. They can tell you what is allowed and may enable it for you.
2. Generate SSH Key Pairs
Key-based authentication is more secure than password-only login. Create an SSH key pair (public and private keys) on your local machine and protect the private key carefully.
- Creating Keys: Run
ssh-keygenin your terminal to generate an SSH key pair. This creates a public key file (for example,id_rsa.pub) and a private key file (for example,id_rsa). Never share your private key. - Passphrase: When prompted, add a passphrase to your private key for an extra layer of security. A passphrase helps protect the key if the private key file is compromised.
3. Upload Your Public Key to the Hosting Account
After generating your public key, you must add it to your hosting account so the server recognizes your key for authentication.
- Via Control Panel: In cPanel, look for “SSH Keys” and use the “Upload Public Key” option to paste the contents of your
id_rsa.pubfile. - Manual Upload: If your control panel does not provide an upload interface, use
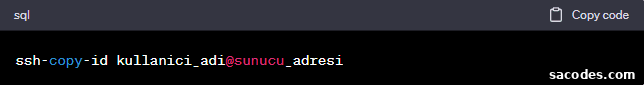
ssh-copy-idor manually append your public key to the server’s~/.ssh/authorized_keysfile.
4. Test Your SSH Connection
Once the public key is installed, verify the connection from your terminal. Use the standard SSH command and point it to your server hostname or IP and username.
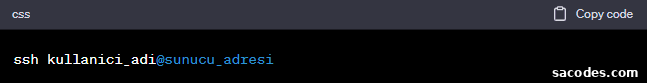
If configured correctly, you should be able to log in using your key (and passphrase, if set) without entering the account password. Successful key-based login confirms SSH access is working.
In short, enabling SSH access on Linux hosting makes server management more secure and efficient. Use SSH carefully: commands run as the wrong user or with root privileges can cause permanent changes to your system.
Common SSH Tasks and Security Recommendations
SSH not only secures your connection but also enables a variety of administrative tasks. Below are common uses and best practices to harden your Linux hosting environment.
Common Tasks Using SSH
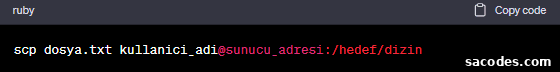
1. File Transfer: Use scp or sftp to transfer files between your local machine and the server securely.
2. Remote Command Execution: Run commands on the remote server to install updates, manage services, or edit configurations.
3. Backups: Use tar or rsync over SSH to create or synchronize backups securely.
4. Database Management: Access command-line tools like mysql or pgsql via SSH for direct database management.
5. Monitoring: Monitor server performance with tools like top or htop through an SSH session.
SSH Security Best Practices
- Use Key-Based Authentication: Prefer SSH keys over passwords to reduce the risk of brute-force attacks.
- Change the Default SSH Port: Moving SSH from port 22 to a non-standard port can reduce automated attack traffic.
- Disable Root Login: Prevent direct root access via SSH. Log in as a regular user and escalate with
sudowhen needed. - Protect Against Brute Force: Tools like
Fail2Bancan block IP addresses after repeated failed attempts. - Hide SSH Version/Banner: Suppress version banners to avoid revealing software details to potential attackers.
- Enable Two-Factor Authentication: Add 2FA for an extra layer of protection even if credentials are compromised.
- Keep Software Updated: Regularly update the SSH server and other system packages to patch vulnerabilities.
Conclusion: When configured and used correctly, SSH is a powerful and secure tool for managing Linux hosting environments. Follow the setup steps and implement the recommended security practices to maintain a robust, manageable server setup without exposing unnecessary risks.